Reference library

Reference library: compliance in practice

Practice-based reference concepts that are too detailed for a public page. Request access for free; after a personal review you receive an access code that is valid for 3 days.

How we handle any compliance request

Five steps, the same for every rulebook. Each step ends with a document you can show to your customer or auditor.

  1. Scope and requirementsResult: Requirements register
  2. Map to one shared control setResult: Mapping matrix
  3. Architecture and controlsResult: Security architecture, threat model
  4. Evidence packResult: Technical file, test reports, SBOM, declarations
  5. Operate: report and updateResult: Incident runbook, vulnerability and update process

One control, many rulebooks

Built once, the same control answers several rulebooks at the same time. Extract, simplified, as of November 2026.

ControlEU CRAChina MLPS 2.0 / CSLIEC 62443ISO/IEC 27001:2022Hong Kong Cap. 653
Access control, strong loginAnnex I Part I (2)(d)Secure computing environment: identification, access control62443-4-2 CR 1.1, CR 2.1A.5.15, A.8.5Code of Practice
Encrypted, tamper-proof communicationAnnex I Part I (2)(e)(f)Secure communication network: transmissionCR 3.1, CR 4.1A.8.20, A.8.24Code of Practice
Network zones, small attack surfaceAnnex I Part I (2)(j)Secure area boundary: boundary protectionCR 5.1, CR 7.7A.8.22Code of Practice
Signed updates, secure bootAnnex I Part I (2)(c)(f)Secure computing environment: trusted verificationCR 3.4, CR 3.10, CR 3.14A.8.19, A.8.32Code of Practice
Logging and monitoringAnnex I Part I (2)(l)Security management centre: audit managementCR 2.8, CR 6.1A.8.15, A.8.16Code of Practice
Vulnerability handling, SBOMAnnex I Part IISecurity operations: vulnerability and risk management62443-4-1 DM, SUMA.8.8Code of Practice
Incident reportingArt. 14: 24 h / 72 hIncident reporting measures: 4 h (CII: 1 h)62443-2-1 incident responseA.5.24–A.5.2612 h serious, 48 h other
Risk assessment and auditArt. 13: risk assessmentGrading, filing, assessment (level 3: yearly)62443-3-2Clauses 6.1.2, 8.2Assessment yearly, independent audit every 2 years

Hong Kong Cap. 653 applies directly to designated critical-infrastructure operators; their suppliers meet it through the operator's requirements. MLPS 2.0 = GB/T 22239-2019; CSL = China Cybersecurity Law as amended from 1 January 2026.

⬇ Capability statement (PDF, 中文 / English)

Available now

Reference library: CRA worked example, regulations EU vs China vs Hong Kong, concepts for China/HK

  • 3 sections
  • 6 + 6 reference concepts
  • 10 diagrams
  • 4 templates EN/中文
  • 63 files
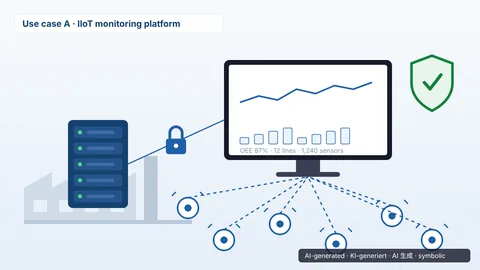
  • Symbolic AI-generated illustration: A · IIoT monitoring platform
    A · IIoT monitoring platform
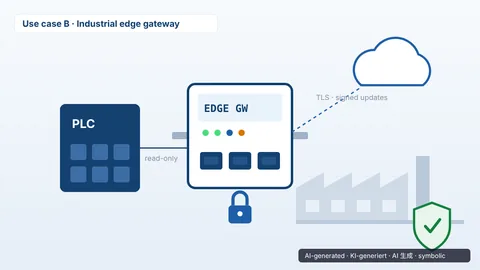
  • Symbolic AI-generated illustration: B · Industrial edge gateway
    B · Industrial edge gateway
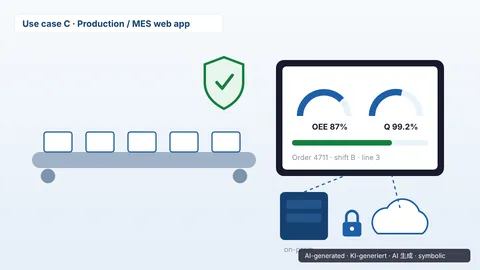
  • Symbolic AI-generated illustration: C · Production/MES web app
    C · Production/MES web app
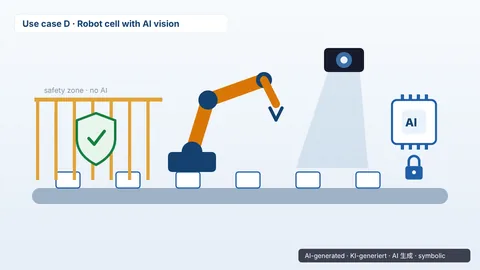
  • Symbolic AI-generated illustration: D · Robot cell with AI vision
    D · Robot cell with AI vision
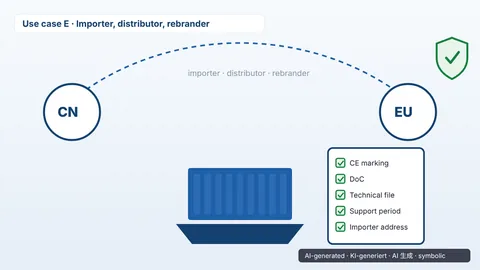
  • Symbolic AI-generated illustration: E · Importer and distributor
    E · Importer and distributor
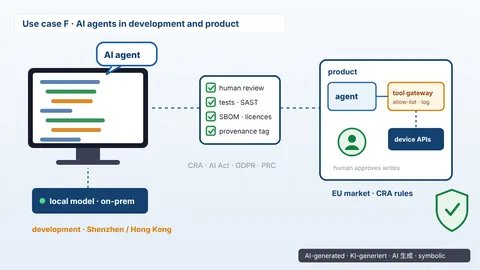
  • Symbolic AI-generated illustration: F · AI agents in development and product
    F · AI agents in development and product

AIPictures: symbolic illustrations, AI-generated (Claude, Anthropic) and labelled as such — transparency under the EU AI Act.

Six complete CRA concepts for IT, automation, production, IoT, robotics, importers and AI-assisted development, built on how Bosch Rexroth, Phoenix Contact, Siemens and KUKA implement the regulation. With a one-page framework diagram, worked examples (risk assessment, SBOM, declaration of conformity, security advisory), development and production in China, a comparison EU/Austria – China – Hong Kong and ready-to-use templates. Reference work, not completed customer projects.

Contents

  • At a glance: one diagram with inputs, steps, outputs, dependencies and context
  • Concept A: on-prem IIoT monitoring platform (default class, self-assessment)
  • Concept B: industrial edge gateway made in China (Class I, notified body)
  • Concept C: production/MES web app, on-prem and cloud
  • Concept D: robot cell with AI vision, PLC and backend (CRA, Machinery Regulation, AI Act)
  • Concept E: importer, distributor or rebrander of a non-EU product
  • Concept F: AI agents in development (Shenzhen/Hong Kong) and in the product, with an informational comparison for European companies
  • Products already on the market: when an update becomes a substantial modification
  • Worked examples: risk assessment, CycloneDX SBOM, declaration of conformity, CSAF security advisory
  • PSIRT and 24 h / 72 h reporting runbook, SBOM pipeline, support periods
  • Development and production in China, concept design "One Centre, Triple Protection" (bilingual)
  • Templates (EN/ZH), normative references, real-life evidence and all sources
  • Regulations section: graphics of what EU, mainland China and Hong Kong regulate at the core, dependency diagram, key facts with sources
  • China/Hong Kong section: concepts A–F transformed for projects in mainland China and Hong Kong (English and Chinese)

Updated: 2026-11-08

Request access →Free · personal approval · code valid 3 days
The same method on request:
  • China MLPS 2.0 (等保2.0)
  • China Cybersecurity Law 2026
  • PIPL / PDPO
  • Hong Kong Cap. 653
  • IEC 62443
  • ISO/IEC 27001
  • EU AI Act
  • NIS2 / NISG 2026
  • Machinery Regulation 2027
Send us your rulebook or your customer's requirement list.

How access works

  1. Send the request form. You immediately receive a ticket ID by e-mail.
  2. We review every request personally, usually within one business day.
  3. After approval you receive a personal access code by e-mail. It is valid for 3 days.
  4. Enter the code on this page (or use the link in the e-mail) to open and download the files.

Request access

I already have an access code

Enter the code from the approval e-mail.

Call usFree initial call